03
Before you buy
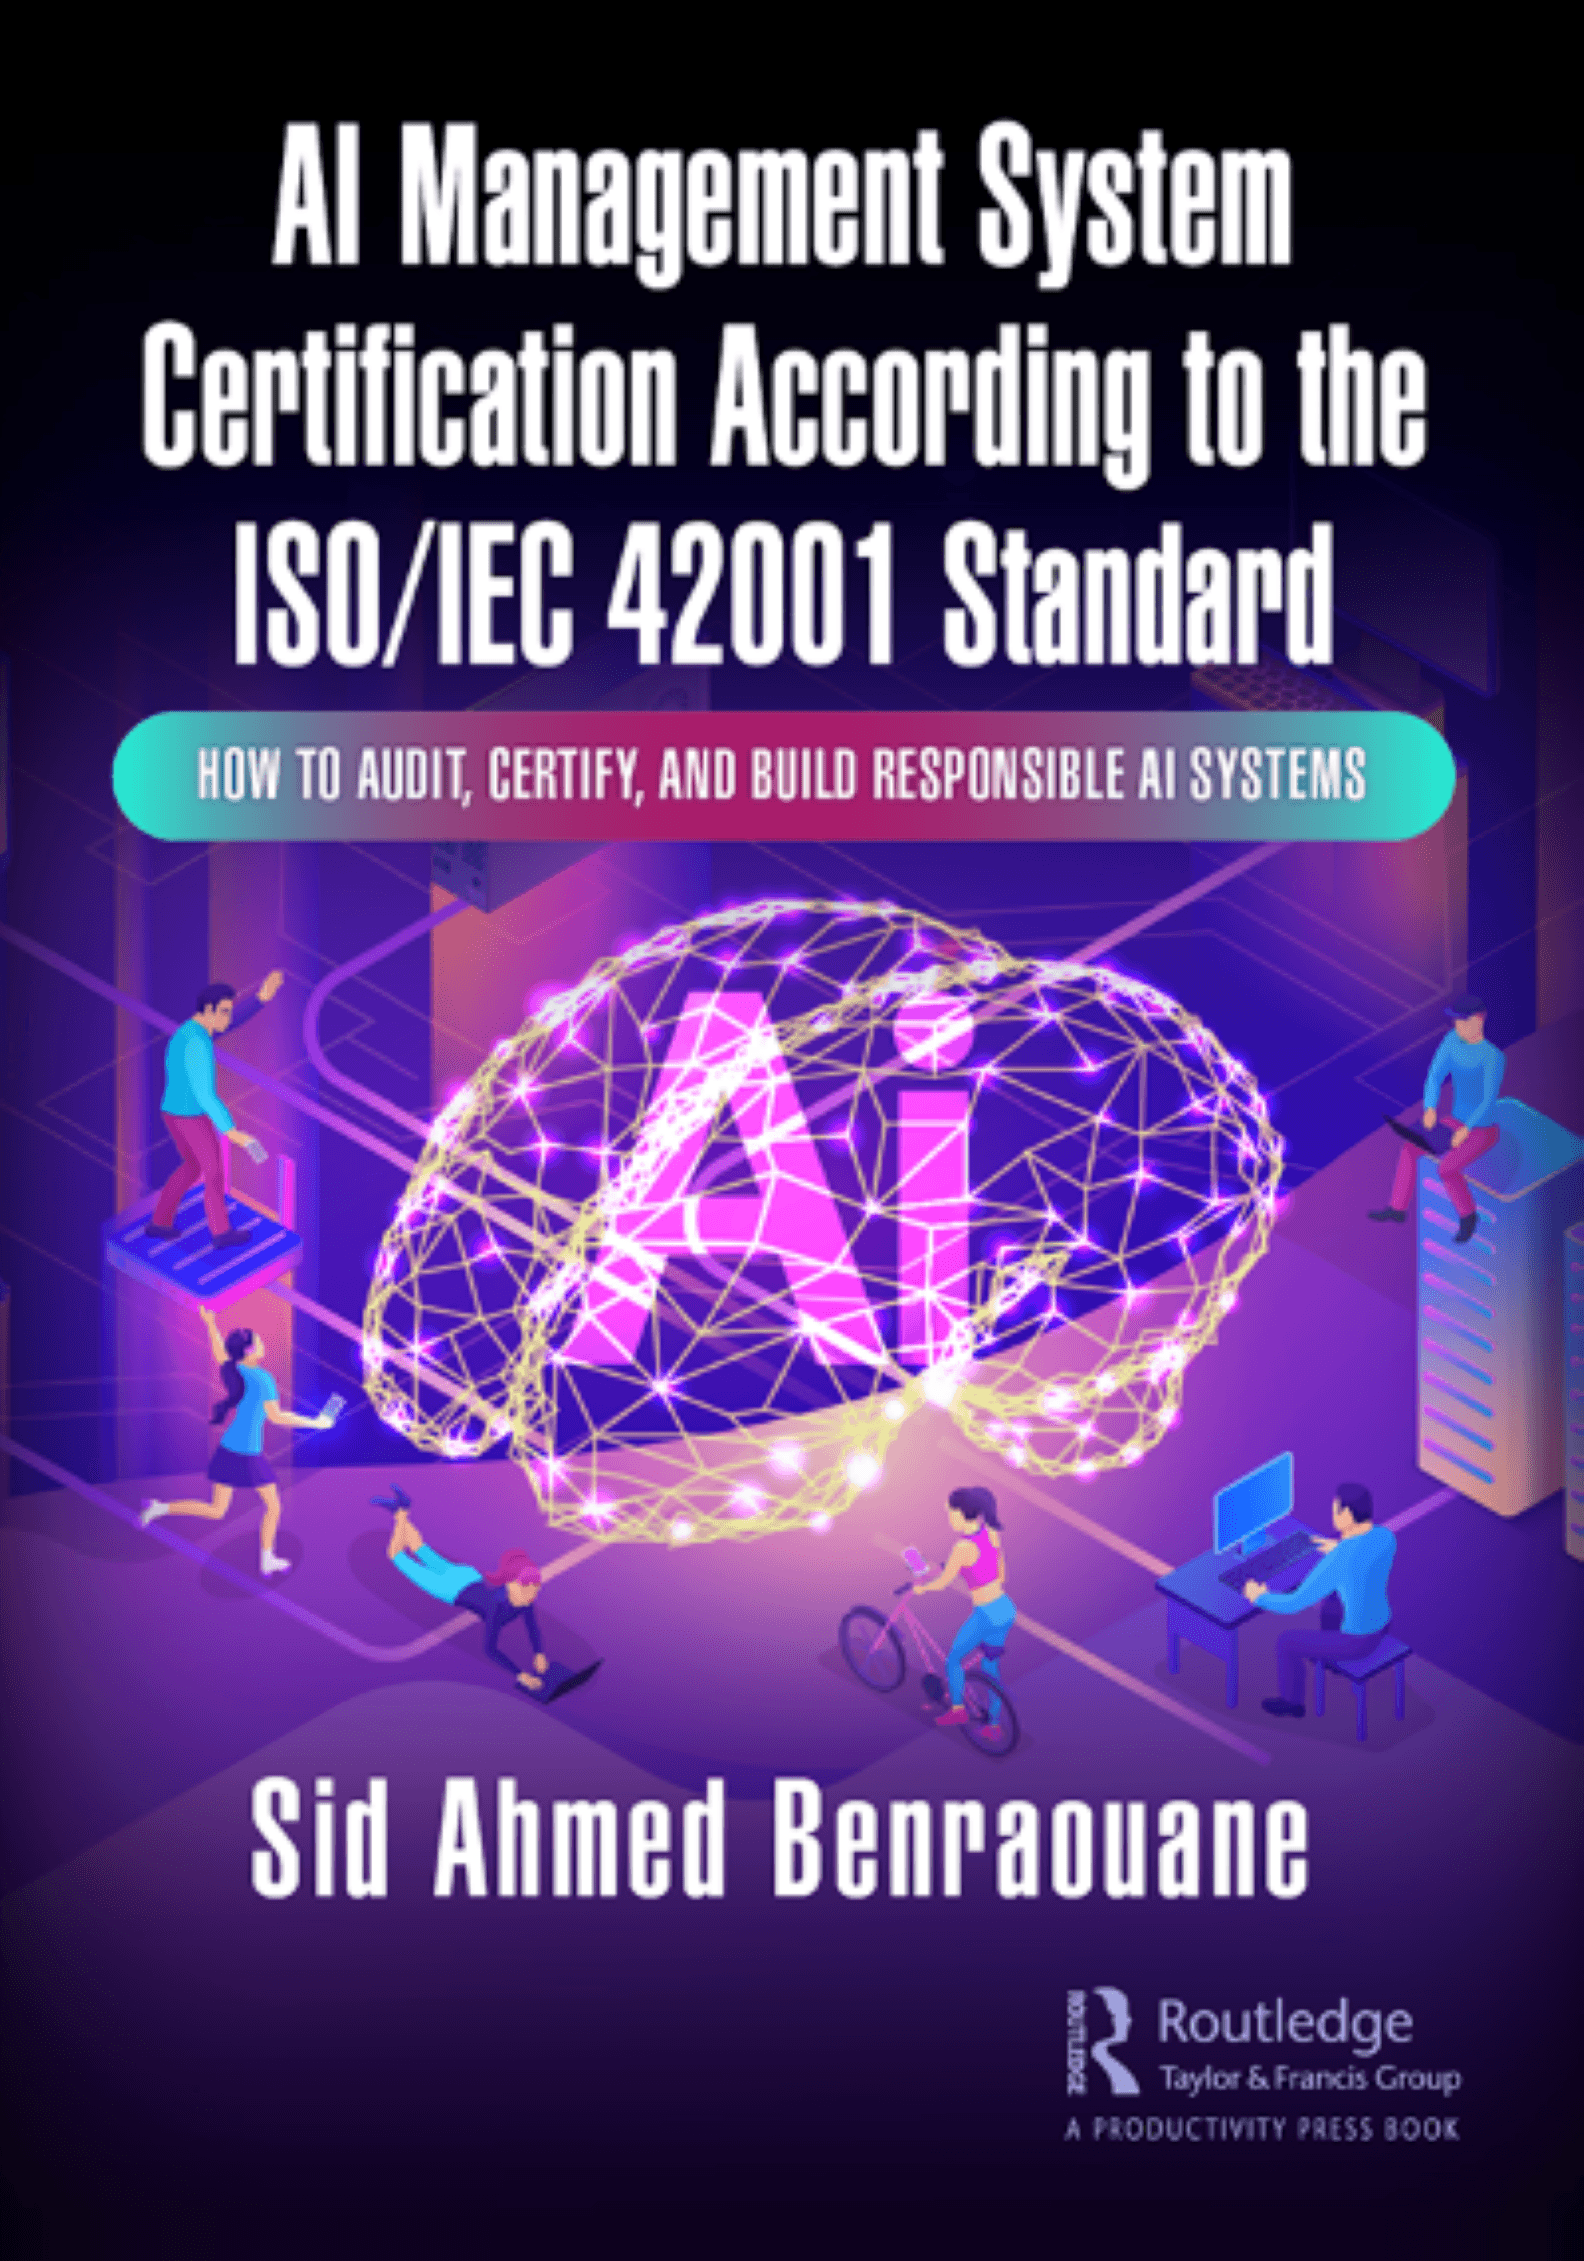
- Does the book go through the standard clause by clause?
- Yes. Part Two dedicates one chapter to each of clauses 4 through 10 — context, leadership, planning, support, operation, performance evaluation, and improvement. That is the bulk of the book.
- Do I still need to buy the standard itself?
- Yes. ISO/IEC 42001 is copyrighted and sold by ISO and national standards bodies, so no book can reproduce it. This one is a companion: it explains what the requirements mean and what satisfying them looks like in practice.
- Is it a technical book? Do I need a machine learning background?
- No. It is written for the people accountable for AI governance — auditors, compliance leads, executives — rather than for the engineers building models. There is no code in it.
- We already hold ISO/IEC 27001. Does that get us most of the way?
- It helps with the management-system mechanics, and 42001 deliberately mirrors the same high-level structure. But the subject matter is different: fairness, transparency, human oversight, impact on people, and model behavior over time have no equivalent in an information security management system.
- Is it useful before we start certification, or only during the audit?
- Before. Most of the value is in the preparation — deciding scope, building the risk and impact registers, and establishing oversight — all of which is far cheaper to get right ahead of a Stage 1 audit than to repair after one.
- Does it cover the EU AI Act and other regulation?
- Yes. Alongside the standard itself, the book covers how to read the EU AI Act and its conformity assessment requirement, and touches on U.S. legislation such as New York City Local Law 144. The connective tissue is the point: certification under 42001 is how many organizations will demonstrate what regulators are starting to require.
- Where can I buy it?
- From Routledge directly, from Amazon in hardcover, paperback and Kindle, and through the usual academic and professional booksellers.